Modern web browsers have become powerful platforms where users manage accounts, communicate, complete financial activities, store information, and access important online services. Because browsers handle so much sensitive activity, security researchers study how browser-based attacks work and how defenders can detect and prevent them.
One security framework often discussed in this area is the Browser Exploitation Framework, commonly known as BeEF. BeEF is a penetration testing tool designed to demonstrate browser security weaknesses in controlled environments. It focuses on browser-side vulnerabilities and shows security professionals how attackers may attempt to interact with compromised browser sessions.
The concept of “persistence” in BeEF discussions refers to maintaining interaction with a browser session after an initial connection has been established. Understanding this concept is important for cybersecurity professionals because it helps explain how browser-based threats operate, what risks exist, and how organizations can strengthen their defenses.
This article explains BeEF persistence from a security awareness perspective, including what browser sessions are, why persistence matters, common defensive challenges, detection methods, and best practices for reducing browser-based security risks.
What Is BeEF?
BeEF stands for Browser Exploitation Framework. It is an open-source security testing framework created for authorized penetration testing and security research.
Unlike traditional security tools that focus mainly on servers, networks, or operating systems, BeEF focuses on the browser as an attack surface. Modern browsers execute large amounts of client-side code, including JavaScript, extensions, and web applications. These features improve user experience but also create opportunities for security testing.
Security professionals may use BeEF in controlled environments to:
- Understand browser security weaknesses
- Demonstrate client-side risks
- Test security awareness
- Evaluate defensive controls
- Study how browser-based threats affect users
The purpose of tools like BeEF is not to compromise random users but to help organizations identify weaknesses before real attackers exploit them.
Understanding Browser Sessions
To understand persistence, it is important to first understand browser sessions.
A browser session represents the period when a user interacts with websites through a browser. During this time, websites may maintain user state through technologies such as:
- Cookies
- Authentication tokens
- Local browser storage
- Session identifiers
- Temporary application data
For example, when a user logs into an online service, the website needs a way to remember that the user has already authenticated. Instead of requiring a password on every page, the website uses session management mechanisms.
These mechanisms are convenient but also security-sensitive. If a session is improperly protected, an attacker may attempt to abuse it.
This is why session security is a major topic in web application security.
What Does Persistence Mean in Browser Security?
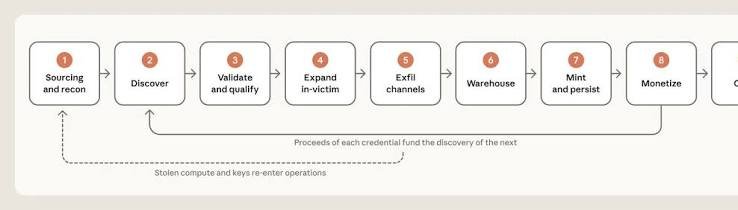
In cybersecurity, persistence generally means maintaining access or communication after an initial compromise or connection.
In browser security discussions, persistence can describe the ability of a browser-based interaction to continue beyond the original moment when the connection was created.
However, browser environments are different from traditional computer systems. Browsers are designed to protect users by limiting what websites and scripts can do. Modern security features, privacy controls, and browser updates make long-term unauthorized browser control difficult.
Persistence in browser contexts depends on many factors, including:
- Browser security settings
- User behavior
- Website security controls
- Session management practices
- Device protections
- Security monitoring capabilities
A secure browser environment should make unauthorized persistence difficult.
How Browser-Based Threats Attempt to Maintain Access
Browser-based threats generally rely on weaknesses in how users, websites, and applications interact.
Some common risk areas include:
Weak Session Management
Poorly designed session systems may expose users to risks. Examples include insecure handling of authentication information, weak expiration policies, or improper protection of sensitive tokens.
Strong session management reduces opportunities for attackers.
Unsafe Browser Extensions
Browser extensions can add useful functionality, but poorly designed or malicious extensions may introduce security problems.
Users should carefully review:
- Extension permissions
- Developer reputation
- Installation sources
- Update history
Social Engineering
Many browser-based attacks depend more on human behavior than technical weaknesses.
Attackers may attempt to trick users into:
- Visiting unsafe websites
- Installing suspicious software
- Entering credentials into fake pages
- Ignoring security warnings
Security awareness remains one of the strongest defenses.
Outdated Software
Browsers and extensions receive frequent security updates because vulnerabilities are discovered regularly.
Using outdated software increases exposure to known security issues.
Why Persistence Matters for Security Teams
Security teams study persistence because short-lived attacks and long-term attacks create different challenges.
A temporary malicious activity may disappear quickly, while persistent activity may allow attackers more time to:
- Gather information
- Observe user behavior
- Attempt further compromise
- Avoid detection
Understanding persistence helps defenders build stronger security strategies.
Security professionals often ask questions such as:
- How long could unauthorized activity continue?
- What evidence would remain?
- Which monitoring systems would detect unusual behavior?
- How quickly could access be removed?
These questions help organizations improve incident response planning.
The Role of BeEF in Security Testing
BeEF is mainly valuable as a learning and testing framework.
Ethical security professionals may use it to demonstrate browser risks in authorized environments. These tests can help organizations understand issues such as:
- Browser trust boundaries
- Client-side security limitations
- User awareness weaknesses
- Web application security problems
A responsible security assessment always requires permission, clear scope, and controlled testing conditions.
Using security tools against systems without authorization can create legal and ethical problems.
Browser Security Features That Reduce Risks
Modern browsers include many protections designed to limit malicious activity.
Important browser security features include:
Same-Origin Security
Browsers separate websites from each other using security boundaries. This prevents one website from freely accessing another website’s private information.
Content Security Policy
Content Security Policy (CSP) helps website owners control which resources browsers are allowed to load.
A properly configured CSP can reduce certain types of client-side attacks.
Secure Cookies
Websites can use security settings for cookies to reduce unauthorized access risks.
Important protections include:
- Secure transmission requirements
- Restricted script access
- Cross-site request protections
Automatic Updates
Modern browsers frequently release security updates. Keeping software updated reduces exposure to known vulnerabilities.
Multi-Factor Authentication
Even if a password becomes compromised, multi-factor authentication adds another security layer.
Common Misunderstandings About Browser Persistence
There are several misconceptions about browser-based persistence.
Myth: A Browser Can Always Be Controlled Permanently
Modern browsers are designed with strong isolation and security controls. Long-term unauthorized control is not automatic and depends on specific weaknesses.
Myth: Closing the Browser Always Removes Every Risk
Closing a browser can end many temporary activities, but security depends on the specific situation. Users should still review suspicious extensions, account activity, and device security.
Myth: Only Technical Users Are Targeted
Browser-based threats affect all types of users because many attacks rely on social engineering and unsafe decisions.
How Organizations Can Defend Against Browser-Based Threats
Organizations can reduce browser security risks through a combination of technical controls and user education.
Maintain Updated Browsers
Security updates should be applied regularly across all managed devices.
Control Browser Extensions
Organizations should establish policies for:
- Approved extensions
- Extension permissions
- Installation restrictions
Monitor Unusual Activity
Security teams should watch for:
- Unexpected account behavior
- Suspicious login patterns
- Unusual browser activity
- Security alerts
Train Employees
Security awareness programs should teach employees how to identify:
- Fake websites
- Suspicious links
- Unsafe downloads
- Social engineering attempts
Use Strong Authentication
Organizations should implement:
- Multi-factor authentication
- Strong password policies
- Secure identity management
Browser Session Security Best Practices
Protecting browser sessions requires both website owners and users to follow security practices.
For website developers:
- Use secure authentication systems
- Protect session information properly
- Implement appropriate security headers
- Regularly test applications
For users:
- Avoid unknown downloads
- Keep browsers updated
- Review extension permissions
- Use trusted websites
- Enable additional account security features
The Importance of Responsible Security Research
Security research plays an important role in improving digital safety.
Frameworks like BeEF allow researchers and defenders to understand browser security challenges. However, responsible use is essential.
Good security research includes:
- Permission from system owners
- Controlled testing environments
- Clear objectives
- Responsible reporting
The goal of security testing should always be improving protection, not causing harm.
Future of Browser Security
Browser security continues to evolve as online applications become more advanced.
Future improvements may include:
- Stronger isolation technologies
- Better privacy controls
- Improved extension security
- More advanced threat detection
- Stronger authentication systems
As browsers become more powerful, security research will remain important for identifying weaknesses and improving protection.
Frequently Asked Questions
What is BeEF used for?
BeEF is a browser security testing framework used by authorized security professionals to study browser-related vulnerabilities and demonstrate client-side security risks.
Is BeEF a virus?
No. BeEF itself is a security testing framework. Like many cybersecurity tools, its impact depends on how it is used.
What does persistence mean in cybersecurity?
Persistence means maintaining access, communication, or activity after an initial compromise or connection.
Can modern browsers prevent browser-based attacks?
Modern browsers include many security protections, but no technology can eliminate every risk. Safe browsing habits and proper security practices remain important.
Why do security professionals study browser sessions?
Browser sessions often contain access to important online services. Understanding session security helps organizations protect users and applications.
How can users improve browser security?
Users can improve browser security by keeping software updated, avoiding suspicious downloads, reviewing extensions, and using strong authentication methods.
Conclusion
BeEF persistence is an important concept in browser security because it highlights the challenges of protecting modern web environments. Browsers have become central to daily digital activities, making their security a major concern for individuals and organizations.
Understanding how browser sessions work, why persistence matters, and what security controls exist helps defenders prepare against evolving threats. Tools such as BeEF provide valuable learning opportunities when used responsibly in authorized security testing environments.
The strongest protection comes from combining secure software practices, updated technology, user awareness, and effective monitoring. Browser security is not based on one single solution; it requires continuous improvement and a complete approach to protecting users and digital systems.